Conducting a Supply Chain Risk Assessment Before the Next Disruption Hits
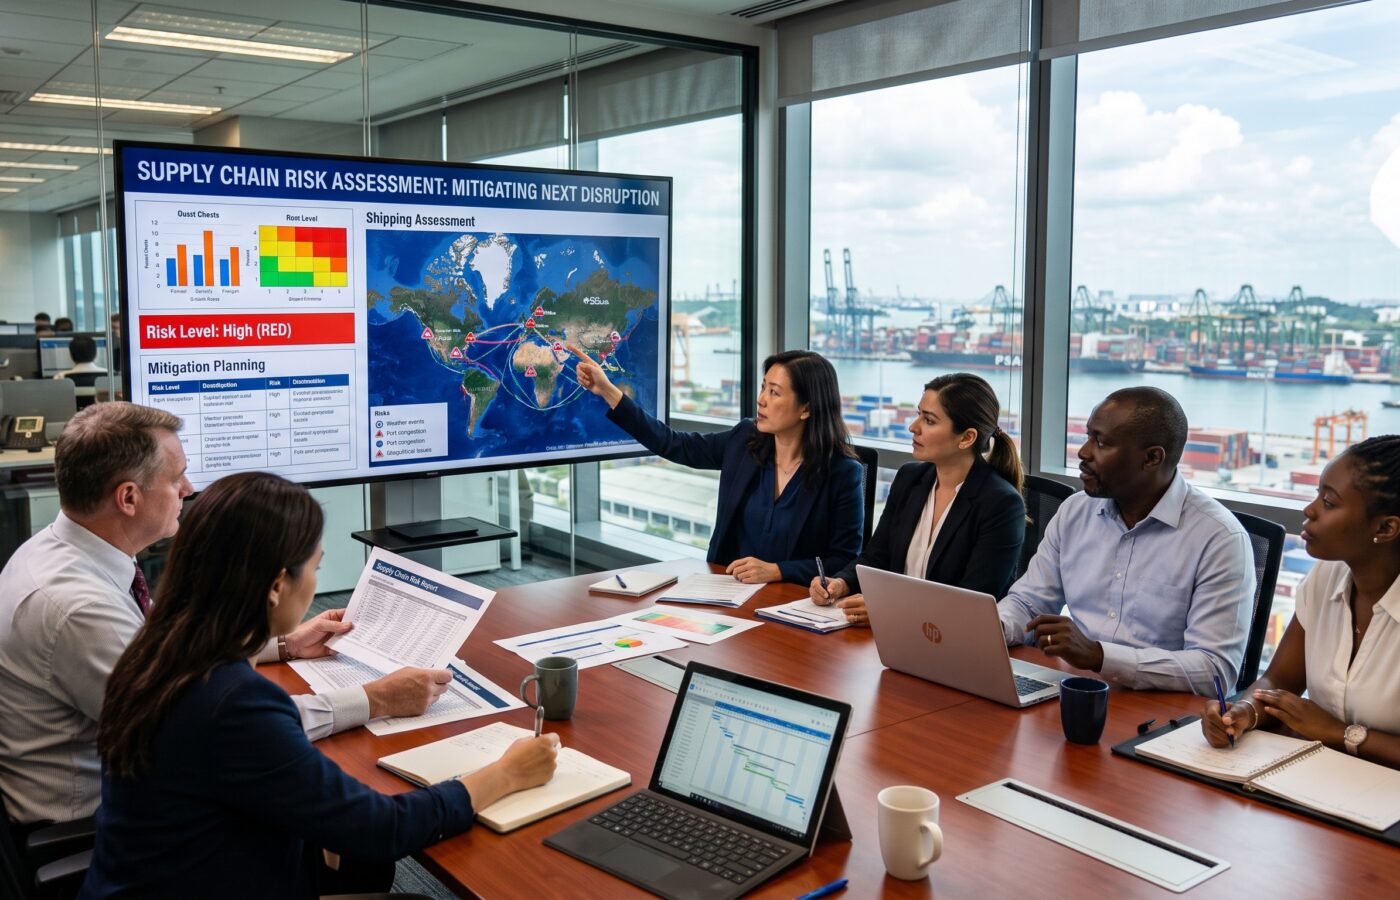
Performing a thorough supply chain risk assessment is the single best way to protect your business from costly operational disruptions. By proactively mapping your dependencies and scoring vulnerabilities, you can identify single points of failure before a crisis hits. In this guide, you will learn a practical, step-by-step framework to evaluate risk, protect your revenue, and build true supply chain resilience.
I still remember the call. It was 2:47 in the morning. The plant manager on the other end of the line told me our second-largest resin supplier had caught fire in their warehouse three hours earlier. We found out from a local news alert before we found out from the supplier. That gap, the one between when something breaks and when you hear about it, is where most companies lose the game. A proper supply chain risk assessment closes that gap. It does not make disruptions disappear. Nothing does. But it changes whether you’re reacting in a panic or executing a plan you already rehearsed.
That fire cost us about eleven days of reduced output on one product line. It could have cost six weeks instead. We’d already mapped that supplier as a single point of failure a year earlier, though, and lined up a backup source. That’s the whole argument for doing this work before you need it, not after.
What a supply chain risk assessment actually involves
People hear “risk assessment” and picture a spreadsheet with red, yellow, and green cells. That’s part of it, sure, but the spreadsheet is the output, not the process. The process is closer to an audit crossed with detective work. You’re trying to answer three questions for every supplier, facility, and transportation route that matters to your operation. What could go wrong here? How likely is that? What would it cost us if it happened tomorrow?
The mistake I see constantly, especially with teams new to this, is starting with a template pulled off the internet and trying to fill in the blanks. Templates are fine as a checklist, but somebody built them around a different supply chain than yours. Ours had a heavy dependency on a handful of Southeast Asian component makers. We had almost no exposure to ocean freight congestion on the transpacific lanes, because we shipped mostly by air for that category. A generic template would have had us assessing container port risk we barely carried. Meanwhile it would have glossed over a supplier concentration problem that actually mattered.
So the real first step is mapping. Not guessing, mapping. Pull your bill of materials, your supplier list, and your logistics providers. Lay out every node between raw material and finished product. Most companies are shocked at how little visibility they have past their tier one suppliers. You might know your direct supplier well, but do you know where they get their inputs? A lot of the disruptions that actually hurt come from tier two or tier three. Those are places you never had a direct relationship with, so you never had a contract clause or an alternate source lined up either.
Scoring risk without fooling yourself
Once you have the map, you score it. I’ve used the same framework across three different companies now, and it shows up in a lot of the serious research on this too. It breaks risk into three dimensions. How bad would it be if it happened? How likely is it to happen? And how prepared are you, right now, to absorb it? McKinsey’s operations team has written about this exact structure. It lines up with what I built independently, which tells me it’s not a fluke. It’s just how the math of risk works once you strip away the jargon.
Where teams get the scoring wrong
Here’s where teams get it wrong. They score likelihood using gut feeling instead of data. Then they score impact using only direct costs and ignore the secondary damage. A two week delay on a single component might cost very little in expedited freight fees. It might also cost you a major customer, if that component happens to be the bottleneck for an order they’ve been waiting on. Impact scoring has to include the downstream commercial consequence, not just the line item on a purchase order.
I also push teams to score their own preparedness honestly, and this is the part people avoid. It’s uncomfortable to write down “we have no backup supplier and no safety stock for this part” next to a critical component. But that discomfort is the entire point of the exercise. If the assessment doesn’t make somebody in a leadership meeting a little nervous, it probably wasn’t honest.
The fastener that almost got missed
A quick example from a category we assessed last year: a specialty fastener. It showed up in maybe four percent of our finished goods by volume, but our highest margin product line needed it in every single unit. Low volume risk on paper. High commercial impact in reality. That fastener came from a single tooling source in a region with real geopolitical tension building. We rated it a top five risk on the entire register, and a lot of people initially pushed back because “it’s such a small part.” Six months later, export controls tightened in that region. Two competitors we know of had to redesign products around that exact fastener family. We didn’t, because we’d already qualified a second source the year before.
Building the risk register and keeping it alive
The document that comes out of this process, the risk register, is only useful if somebody actually opens it. I’ve inherited beautifully built, color coded, thorough registers from predecessors. Every one of them was completely dead. Nobody had touched them in eighteen months. A risk register nobody reviews on a schedule isn’t a management tool. It’s an archive.
What works, at least for the teams I’ve run, is a monthly review of the top tier risks and a quarterly review of everything else. The monthly review takes maybe forty five minutes. You’re not redoing the whole assessment every time. You’re asking whether anything has changed. Did a supplier’s financial health take a hit? Has a region’s political situation gotten more volatile? Did a new customer order concentrate more of your revenue onto a product with a fragile supply base? Small check ins catch drift long before it becomes a crisis.
I’d also say this, and it took me longer to learn than I’d like to admit: the register needs an owner for each risk. A specific person, not a department. “Procurement owns supplier risk” sounds fine until something happens and three different procurement managers each assumed someone else was tracking it. Put a name next to every entry. People act differently when their name is attached to a gap.
Mistakes that quietly wreck a risk assessment program
I’ve made most of these myself, so I say this without much judgment.
Treating the first pass as the finish line
Teams put enormous effort into the initial assessment, present it to leadership, get some applause, and then move on to the next initiative. Six months later nobody remembers the register exists. The assessment is worthless the moment it stops reflecting reality, and reality moves fast in this line of work.
Scoring risk without the people who live it
I’ve seen analysts build entire risk registers from spreadsheets and public data alone, with no input from the buyer who talks to that supplier every week. That buyer already knows their plant had layoffs last quarter, and their gut instinct, informed by dozens of small signals nobody wrote down anywhere, is worth more than most external data sources you can buy. Build the assessment with the operators, not just for them.
Confusing risk assessment with a compliance checklist
Plenty of industries require some version of supplier risk documentation for audit purposes, and it’s tempting to build the whole program around satisfying that requirement. A compliance-driven register tends to be thorough on paper and useless in practice. Teams build it to answer an auditor’s question, not the one that actually matters: what happens to our business if this goes wrong. Compliance can be a byproduct of a good program. It shouldn’t be the design goal.
Underestimating how long mitigation actually takes
This is probably the most expensive mistake. Teams flag a single-source risk, feel good about having identified it, and then treat the fix as a someday project. Qualifying a new supplier, especially for regulated components or anything requiring tooling, routinely takes six to twelve months. If you wait until the primary supplier actually fails before starting that clock, the assessment didn’t buy you anything.
The current environment makes this harder, not optional
I’d be lying if I said the last few years have made this job easier. Tariff policy has shifted multiple times, and every shift ripples through sourcing decisions that took months to finalize. Industry coverage keeps flagging tariff driven disruption as one of the defining challenges this year. Real material constraints are piling on top of it too. Categories like semiconductors, critical minerals, and even food inputs are feeling the squeeze, especially for companies with packaging or agricultural exposure. On top of that, ocean and trucking capacity has been anything but stable. It keeps swinging between overcapacity and tight crunches, depending on the lane and the season.
None of that is an argument for waiting until things settle down before you do a risk assessment. Things aren’t going to settle down in any permanent sense. Volatility is the operating environment now, not a temporary condition to wait out. Companies that treat risk assessment as a project for later are the ones calling their customers with bad news.
I’ll say this too, because not enough people say it. A supply chain risk assessment is not a cybersecurity exercise, even though vendor pitches constantly lump the two together. Cyber risk from third parties matters, and it belongs somewhere in your program. But if your entire risk assessment is really just a vendor security questionnaire wearing a supply chain label, you’re missing plenty. Physical disruption, financial instability at suppliers, geopolitical exposure, labor disputes, and logistics fragility all fall outside that lens. Those categories have caused far more of the disruptions I’ve personally dealt with than a data breach ever has.
Technology helps, but it doesn’t replace judgment
Every year there’s a new platform promising to automate the whole process with dashboards and predictive alerts. Some of these tools are genuinely useful, especially for monitoring leading indicators across dozens or hundreds of suppliers at once. That’s not something a person can do manually at scale. Weather pattern tracking near supplier facilities, financial health scores, and news monitoring for the regions where your suppliers operate: software handles these things better and faster than a team of analysts ever could.
What software doesn’t do well is the judgment call about what actually matters to your specific business. I’ve sat through vendor demos where the tool flags forty risk alerts a week for a mid-size supplier base. Within a month, teams start ignoring the dashboard entirely because it’s noise. The technology is a force multiplier for a program that already has good judgment behind it. It’s not a substitute for someone who understands your commercial exposure well enough to know what’s signal and what’s noise.
If you’re just starting out, don’t lead with a software purchase. Lead with the mapping and scoring exercise using whatever tools you already have, even a well organized spreadsheet. Prove the process works and find out where manual monitoring is genuinely a bottleneck before you go shopping for a platform. I’ve seen too many teams spend their budget on tools that automated a process they hadn’t actually figured out yet.
Getting the rest of the organization to care
Here’s the part nobody warns you about when you take on a risk management role. The hardest part of the job usually isn’t the analysis. It’s convincing a plant manager, a sales VP, or a finance director of something hard to sell. A risk that hasn’t happened yet still deserves budget and attention right now. Risk mitigation competes against initiatives with visible, immediate returns, and it usually loses that argument unless you can tell the story well.
What’s worked for me is translating every risk into a business consequence that person specifically cares about. Finance doesn’t respond to “supplier concentration risk.” It responds to numbers. Something like, “If this supplier goes down, we lose access to the inventory covering forty percent of our Q3 revenue commitment for this customer. A forty five day delay costs this much in penalty clauses.” Sales cares about customer relationships, so frame it around which accounts get hurt. Operations cares about throughput, so frame it around downtime. Same underlying risk, different framing depending on the room you’re in.
I also make a point of bringing at least one real story to every presentation. Ideally it’s something that happened to a competitor or a company in an adjacent industry everyone would recognize. Abstract risk percentages don’t move people the way a specific, concrete story does. That fire I mentioned at the start of this article has shown up in more internal presentations than I can count. It’s real, it’s recent enough to feel relevant, and everyone in the room can picture themselves getting that same 2 a.m. call.
Where teams should actually start this quarter
If someone handed me a blank slate tomorrow and told me to build a supply chain risk assessment program from nothing, here’s roughly the order I’d work through it.
- Map your critical products, the ones responsible for the bulk of your revenue or margin. Trace their full bill of materials as far back as you can get visibility, not just to your direct suppliers.
- For every node in that map, gather basic risk data. That means single source versus multi source, geographic concentration, and financial stability signals if you can get them. Also note lead time for a replacement if that node failed tomorrow.
- Score everything on impact, likelihood, and current preparedness. Be brutally honest on that last one.
- Take the top fifteen to twenty highest risks. Build a specific mitigation plan for each: qualify a second supplier, hold more safety stock, or renegotiate contract terms.
- Assign an owner and a review cadence, and put it on the calendar. It won’t happen on its own.
None of that requires new software or a big budget. It requires time, organizational buy in, and a willingness to write down uncomfortable truths about where you’re exposed. The companies that do this well aren’t the ones with the fanciest tools. They’re the ones who treat it as a living discipline, not a document someone builds once and forgets.
Final thought
A supply chain risk assessment won’t stop the next fire, the next port slowdown, or the next round of tariff changes from happening. What it does is different. It makes sure that when one of those things happens, and something will happen, you find out from your own monitoring. Not from a news alert three hours later. You’re already three steps into a plan you built while things were still calm. That difference, between reacting and executing, is worth every uncomfortable meeting it takes to get there.
Frequently Asked Questions
How often should a supply chain risk assessment be updated?
Top tier risks deserve a monthly check in, while the full register should get a complete review at least quarterly. Major events, such as a new tariff announcement or a supplier bankruptcy filing, should trigger an immediate reassessment of anything connected to that situation. The Gartner supply chain risk research hub covers how leading organizations structure ongoing risk monitoring rather than treating it as an annual exercise.
What’s the difference between supply chain risk assessment and supply chain risk management?
Assessment is the identification and scoring process, the part where you figure out what could go wrong and how bad it would be. Management is everything that happens after: mitigation planning, monitoring, and response when a risk actually materializes. Assessment feeds management, but they’re not the same activity, and treating them as one step is a common early mistake.
Do small and mid-size manufacturers really need a formal risk assessment process?
Yes, arguably more than large enterprises, because smaller companies typically have less supplier redundancy and thinner cash reserves to absorb a shock. A formal process doesn’t require a large team or expensive software. It requires discipline and a willingness to map dependencies honestly. Supply Chain Dive’s ongoing coverage of supply chain risks and trends is a useful way for smaller teams to stay current without a dedicated research staff.
What are the most commonly overlooked risks in a supply chain risk assessment?
Tier two and tier three supplier exposure is the most common blind spot, since most companies only have real visibility into their direct suppliers. Single tooling sources for seemingly minor components slip through often too. So do supplier financial instability and concentration of a critical input in one geographic region.
Can a supply chain risk assessment be done without specialized software?
Yes, and it should start that way. A well maintained spreadsheet with a clear scoring methodology can carry a program a long way before software becomes necessary. Software adds the most value once you already know what you’re monitoring and simply need to do it at a scale a person can’t manage manually.
References
- McKinsey & Company, “A practical approach to supply-chain risk management,”
- Gartner, “Top Supply Chain Risks and Mitigation Strategies,”
- Supply Chain Dive, “Top supply chain risks and trends to follow in 2026,”